Financial Data Protection Act 2026: Redefining Digital Security
Anúncios
The Financial Data Protection Act of 2026 will fundamentally reshape digital account security for millions by establishing robust new standards for financial institutions and enhancing consumer protections.
Anúncios
The digital landscape of finance is constantly evolving, bringing both unparalleled convenience and inherent risks. In 2026, a monumental shift is on the horizon: the introduction of the Financial Data Protection Act. This groundbreaking legislation is set to redefine how digital account security is managed, impacting millions of Americans and fundamentally altering the relationship between consumers, financial institutions, and their sensitive data. Understanding its implications is crucial for everyone navigating the modern financial world.
Anúncios
Understanding the Financial Data Protection Act (FDPA)
The Financial Data Protection Act (FDPA) of 2026 represents a comprehensive legislative effort to bolster digital account security in the United States. Born from increasing concerns over data breaches, identity theft, and the misuse of personal financial information, the FDPA aims to establish a unified and stringent framework for data protection across all financial entities.
This act moves beyond previous fragmented regulations, creating a more cohesive and proactive approach to safeguarding consumer data. It places significant responsibility on financial institutions to not only prevent breaches but also to ensure transparency and accountability in their data handling practices. The FDPA seeks to restore public trust in digital financial services by providing a robust legal foundation for security.
Key Pillars of the FDPA
The FDPA is built upon several core principles designed to address the multifaceted challenges of digital financial security.
- Enhanced Encryption Standards: Mandates the use of state-of-the-art encryption for all sensitive financial data, both in transit and at rest.
- Mandatory Breach Notification: Requires financial institutions to notify affected individuals and regulatory bodies within a specified, short timeframe following a data breach.
- Consumer Consent and Data Usage: Grants consumers greater control over how their financial data is collected, stored, and shared, requiring explicit consent for specific uses.
- Regular Security Audits: Imposes mandatory, independent security audits for all financial entities to ensure compliance and identify vulnerabilities proactively.
In essence, the FDPA is not just about reacting to security incidents but about fostering an environment where prevention and consumer empowerment are paramount. It acknowledges the dynamic nature of cyber threats and aims to future-proof digital financial security as much as possible.
Impact on Financial Institutions: New Responsibilities
For banks, credit unions, fintech companies, and other financial service providers, the Financial Data Protection Act introduces a new era of compliance and operational adjustments. The legislation mandates higher standards for data security, privacy, and incident response, requiring significant investments in technology, training, and policy development.
These institutions will need to re-evaluate their entire data lifecycle management, from collection to destruction, ensuring every step adheres to the FDPA’s stringent requirements. This includes implementing advanced cybersecurity measures, developing sophisticated data governance frameworks, and fostering a culture of data protection throughout their organizations. The cost of non-compliance can be substantial, including hefty fines and reputational damage.
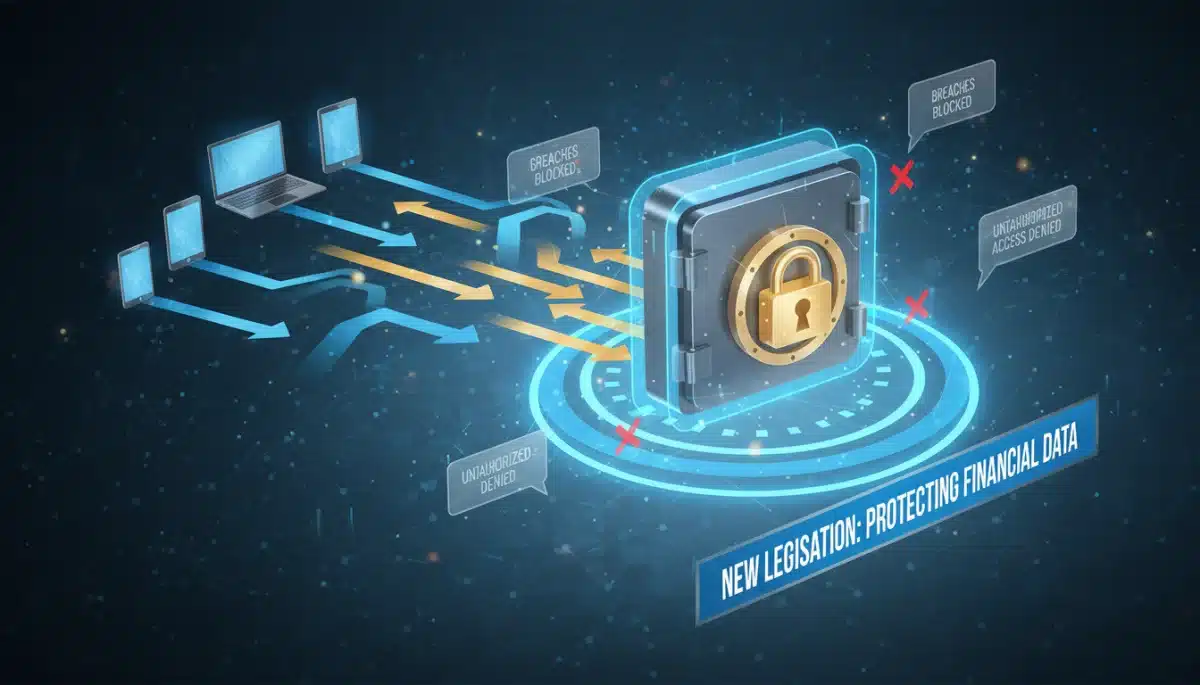
One of the primary challenges will be integrating these new requirements into legacy systems, many of which were not designed with such comprehensive data protection in mind. This will likely drive innovation in financial technology, as institutions seek scalable and secure solutions to meet compliance demands.
Operational Changes and Technology Upgrades
Financial institutions are expected to undertake substantial operational changes and technology upgrades to align with the FDPA. This will involve a multi-pronged approach to security and compliance.
- Advanced Threat Detection: Investing in AI-driven tools and machine learning algorithms to detect and neutralize cyber threats in real-time.
- Data Minimization Principles: Adopting practices to collect and retain only the data absolutely necessary for service provision, reducing the attack surface.
- Employee Training Programs: Implementing mandatory and regular training for all employees on data protection protocols, phishing awareness, and secure handling of sensitive information.
- Incident Response Plans: Developing robust and frequently tested incident response plans to effectively manage and mitigate the impact of data breaches.
The FDPA also encourages collaboration between financial institutions and cybersecurity experts, recognizing that collective intelligence and shared best practices are crucial in combating sophisticated cybercriminal organizations. This shift will likely lead to greater industry-wide cooperation on security matters.
Empowering Consumers: Greater Control and Protection
For millions of consumers, the Financial Data Protection Act signifies a substantial leap forward in personal financial security and privacy. The legislation is designed to put individuals back in control of their sensitive financial information, moving away from opaque data practices towards a model of transparency and explicit consent.
Consumers will gain new rights, including the right to access their data, rectify inaccuracies, and even request the deletion of certain data under specific circumstances. This newfound control empowers individuals to make informed decisions about who has access to their financial information and for what purpose. It aims to build a stronger sense of trust between consumers and the financial institutions they rely upon.
The act also introduces clearer, more understandable privacy policies, moving away from convoluted legal jargon that often leaves consumers confused about their rights and the fate of their data. This emphasis on clarity is a cornerstone of the FDPA’s consumer-centric approach.
New Consumer Rights and Responsibilities
The FDPA outlines several key rights that will empower consumers, alongside some responsibilities to ensure their own digital safety.
- Right to Data Access: Consumers can request and receive a copy of all their financial data held by an institution.
- Right to Rectification: The ability to correct any inaccurate personal financial information.
- Right to Erasure (‘Right to be Forgotten’): Under certain conditions, consumers can request the deletion of their financial data.
- Opt-Out of Data Sharing: Explicit mechanisms for consumers to easily opt-out of their data being shared with third parties for marketing or other non-essential purposes.
While the FDPA provides significant protections, consumers also bear a responsibility to practice good digital hygiene, such as using strong, unique passwords, enabling multi-factor authentication, and being vigilant against phishing attempts. The legislation acts as a strong safety net, but individual awareness remains crucial.
Challenges and Criticisms of the FDPA
While the Financial Data Protection Act is largely seen as a necessary and positive development, its implementation is not without challenges and has drawn some criticism. Financial institutions, particularly smaller ones, may struggle with the significant compliance costs and the complexity of integrating new security protocols. This could potentially lead to consolidation in the industry or increased service fees for consumers.
Another area of concern is the potential for regulatory overlap or conflict with existing state-level data privacy laws. Harmonizing these different legal frameworks will be crucial to avoid confusion and ensure consistent enforcement. Critics also point to the difficulty in keeping pace with rapidly evolving cyber threats, arguing that any legislation, no matter how comprehensive, risks becoming outdated quickly.
Furthermore, defining what constitutes ‘sensitive financial data’ and establishing clear boundaries for its use and sharing can be a contentious issue, leading to ongoing debates and potential legal challenges as the act is put into practice. The balance between strong security and operational efficiency will be a continuous tightrope walk.
Balancing Security, Innovation, and Cost
The FDPA faces the inherent challenge of striking a delicate balance between robust security measures, fostering financial innovation, and managing the associated costs.
- Innovation Stifling: Concerns that overly strict regulations might hinder the development of new financial products and services, especially for agile fintech startups.
- Compliance Burden: The financial and administrative burden on smaller institutions, potentially limiting their competitiveness.
- Enforcement Complexity: The sheer scale and complexity of enforcing the FDPA across a diverse financial ecosystem.
- Data Portability: Ensuring that enhanced security doesn’t inadvertently create barriers to legitimate data portability and interoperability, which can benefit consumers.
Addressing these challenges will require ongoing dialogue between regulators, industry stakeholders, and consumer advocacy groups to refine the FDPA’s implementation and ensure its long-term effectiveness without stifling the growth of the financial sector.
Preparing for 2026: What Individuals and Businesses Should Do
With the Financial Data Protection Act slated for implementation in 2026, both individuals and businesses have proactive steps they can take to prepare for the new regulatory landscape. For individuals, this means becoming more aware of their digital financial footprint and understanding the new rights afforded to them.
For businesses, particularly financial institutions and any entity handling sensitive financial data, preparation involves a comprehensive review of current data security practices, compliance strategies, and technological infrastructure. Early adoption of FDPA-aligned best practices can provide a competitive advantage and minimize disruption once the act comes into full force. Ignoring these changes could lead to significant penalties and loss of customer trust.
The transition period leading up to 2026 is a critical window for education, adaptation, and investment in future-proof security solutions. Proactive engagement will be key to a smooth and successful implementation of the FDPA.
Actionable Steps for Preparedness
Both consumers and businesses can take concrete actions to be ready for the FDPA.
- For Individuals:
- Review privacy policies of financial institutions.
- Enable multi-factor authentication on all financial accounts.
- Monitor credit reports regularly for suspicious activity.
- Understand your new rights regarding data access and deletion.
- For Businesses:
- Conduct a thorough data inventory and risk assessment.
- Update data privacy policies and terms of service.
- Invest in cybersecurity training for all employees.
- Engage legal and cybersecurity experts for compliance guidance.
These proactive measures will not only aid in compliance with the FDPA but also contribute to a generally more secure digital financial environment for everyone involved. The goal is to foster a culture of shared responsibility in protecting sensitive financial data.
The Future of Digital Account Security Post-FDPA
The implementation of the Financial Data Protection Act in 2026 is poised to usher in a transformative era for digital account security. While challenges undoubtedly lie ahead, the long-term vision is one of a more secure, transparent, and consumer-centric financial ecosystem. The FDPA sets a new global benchmark for data protection, potentially influencing similar legislative efforts in other countries.
We can expect to see a continuous evolution in cybersecurity technologies, driven by the act’s stringent requirements. Financial institutions will likely become even more proactive in threat intelligence and prevention, moving towards predictive security models. Consumers, armed with greater rights and awareness, will demand higher standards of data protection, making security a key differentiator for financial service providers.
Ultimately, the FDPA aims to create an environment where the benefits of digital finance can be fully realized without compromising the security and privacy of millions of users. It is a critical step towards building a resilient and trustworthy digital economy.
Long-Term Implications and Evolving Landscape
The FDPA’s influence will extend far beyond its initial implementation, shaping the financial landscape for years to come.
- Increased Trust: Greater consumer confidence in digital financial services, potentially leading to increased adoption and innovation.
- Global Standard: The FDPA could serve as a model for international data protection laws, fostering greater interoperability and consistent security across borders.
- Continuous Adaptation: The need for ongoing legislative updates and technological advancements to counter emerging cyber threats effectively.
- Shift in Business Models: Financial institutions may adapt their business models to prioritize data privacy and security as core offerings rather than mere compliance.
The future of digital account security, post-FDPA, is one of continuous vigilance, innovation, and a collective commitment to protecting the financial well-being of millions. It represents a significant stride towards a safer and more dependable digital financial future.
| Key Aspect | Brief Description |
|---|---|
| Core Purpose | To establish a unified and stringent framework for digital financial data protection in the U.S. |
| Impact on Institutions | Mandates enhanced encryption, regular audits, and robust incident response plans. |
| Consumer Empowerment | Grants rights to data access, rectification, erasure, and explicit consent for data usage. |
| Key Challenges | Compliance costs, regulatory harmonization, and keeping pace with evolving cyber threats. |
Frequently Asked Questions About the FDPA
The primary goal of the FDPA is to enhance digital account security for millions of Americans by establishing comprehensive and unified standards for how financial institutions collect, store, and protect sensitive financial data, minimizing risks of breaches and misuse.
The FDPA will give you greater control over your financial data. You will have rights to access, rectify, and in some cases, request the deletion of your data. It also mandates clearer privacy policies and requires explicit consent for certain data sharing practices.
Financial institutions will face stricter requirements, including mandatory advanced encryption, regular independent security audits, and prompt notification protocols in the event of a data breach. They must also implement robust internal data governance frameworks.
The Financial Data Protection Act is scheduled to come into full effect in 2026. This timeline allows financial institutions and consumers sufficient time to prepare and adapt to the new regulations and enhanced security measures.
Yes, challenges include significant compliance costs for financial institutions, potential regulatory overlap with existing state laws, and the ongoing effort to keep the legislation relevant amidst rapidly evolving cyber threats. Balancing security with innovation is also a key concern.
Conclusion
The Financial Data Protection Act of 2026 marks a pivotal moment for digital account security in the United States. By introducing a robust and unified regulatory framework, it aims to fortify the defenses around sensitive financial data, empower consumers with greater control, and foster an environment of trust and transparency. While its implementation will undoubtedly present challenges for financial institutions, the long-term benefits of enhanced security and consumer confidence are expected to far outweigh the transitional hurdles. As 2026 approaches, proactive engagement from all stakeholders will be crucial in realizing the full potential of this landmark legislation, paving the way for a more secure and resilient digital financial future for millions.
